A self-hosted platform on a handful of Raspberry Pis that gives me secure remote access to everything at home, browser-based desktops, a single login across services, a private Git server, file storage and proper monitoring. Everything is deployed from an Ansible inventory, and the public internet only ever sees a WireGuard port.
Access model
WireGuard is the only way in. Clients get a VPN address and split-tunnel routes for the lab subnets, and a dnsmasq on the WireGuard interface resolves home.lab names so gitea.home.lab works from anywhere. Inside, NGINX on the edge Pi terminates TLS for every web service and proxies to backends over the LAN, so remote traffic rides the tunnel but east-west traffic between services doesn't.
Client devices
    |
    v
WireGuard VPN (ingress only)
    |
    v
Raspberry Pi OS edge host
    |- WireGuard
    |- NGINX reverse proxy
    `- DNS (dnsmasq on wg0)
            |
            v
Internal LAN (192.168.0.0/24)
    +-- service Pis: Guacamole, Gitea, LLDAP, Grafana/Prometheus/Loki, Zabbix
    +-- storage Pi: Samba + RAID
    +-- Windows/Linux hosts: RDP / SSH / VNC targets
    `-- control host: dashboard + Ansible
Services
- LLDAP: the one identity store. Guacamole, Gitea and Semaphore all authenticate against it.
- Apache Guacamole: HTML5 remote desktops, RemoteApps and SSH terminals with no client install. Connections for every Pi (SSH and XRDP desktops) and VNC entries for the Windows machines are seeded from the inventory at deploy time.
- Gitea: private Git hosting, behind NGINX, LDAP login. Every project on this site lives there.
- Samba on RAID: central storage and backups, assembled and mounted at boot.
- Grafana + Prometheus + Loki + Alloy: host and container metrics, blackbox probes of the key endpoints, and centralised logs with pre-provisioned dashboards.
- Zabbix: availability checks, alerting and a live network topology map of how the hosts connect through the VPN.
- Semaphore: a web UI for running the Ansible playbooks, so routine deploys don't need a terminal.
- Nextcloud, Jellyfin, n8n and a few home-grown pages (a text editor, file store, media player and paint app) hang off the same proxy.
Operations
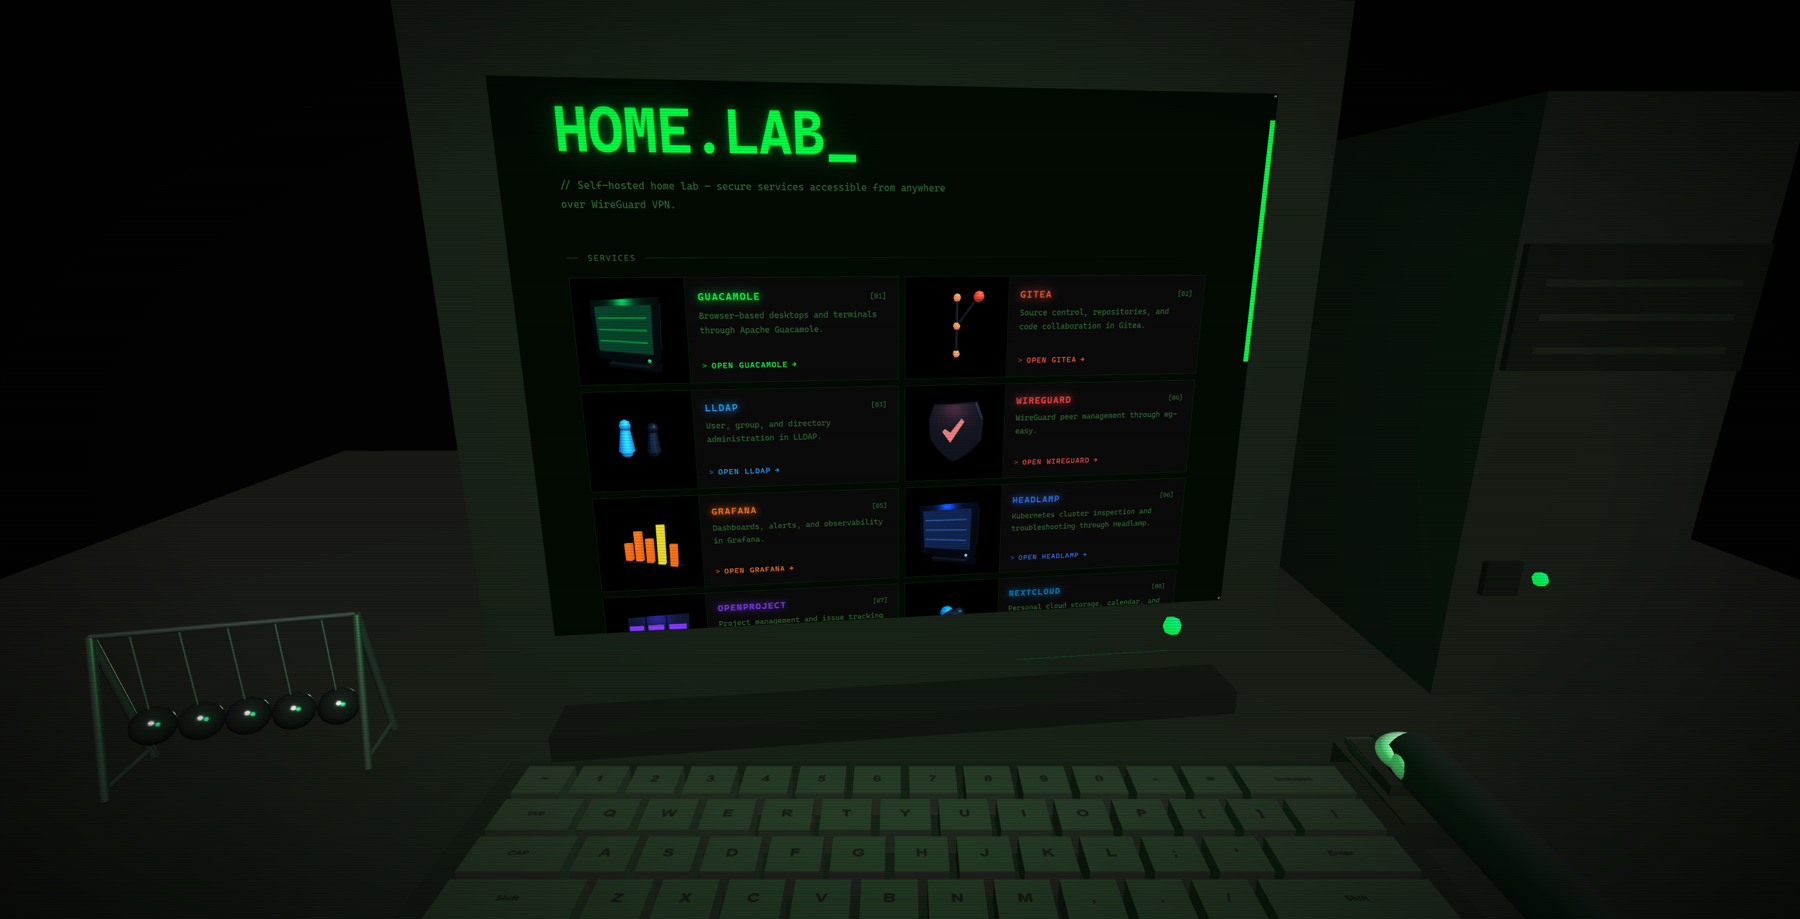
Native services are systemd units with restart policies; containers use Docker restart policies; so the lab comes back on its own after a power cut. A small dashboard on the control host validates the inventory, checks SSH reachability and service health, and triggers the same bootstrap and deploy playbooks I'd run from the shell. The NGINX role also renders the landing page: a three.js desk with a CRT monitor whose screen lists the enabled services as cards. If that sounds familiar, it's because this website is the same design.
Why
Partly to have Git, files and remote desktops without renting them, partly to run the enterprise pattern (VPN ingress, central identity, reverse proxy, observability) at a scale I can hold in my head and rebuild from a repo. The whole thing is low-power, always-on, and documented in a solution architecture document that I keep honest by deploying from it.